
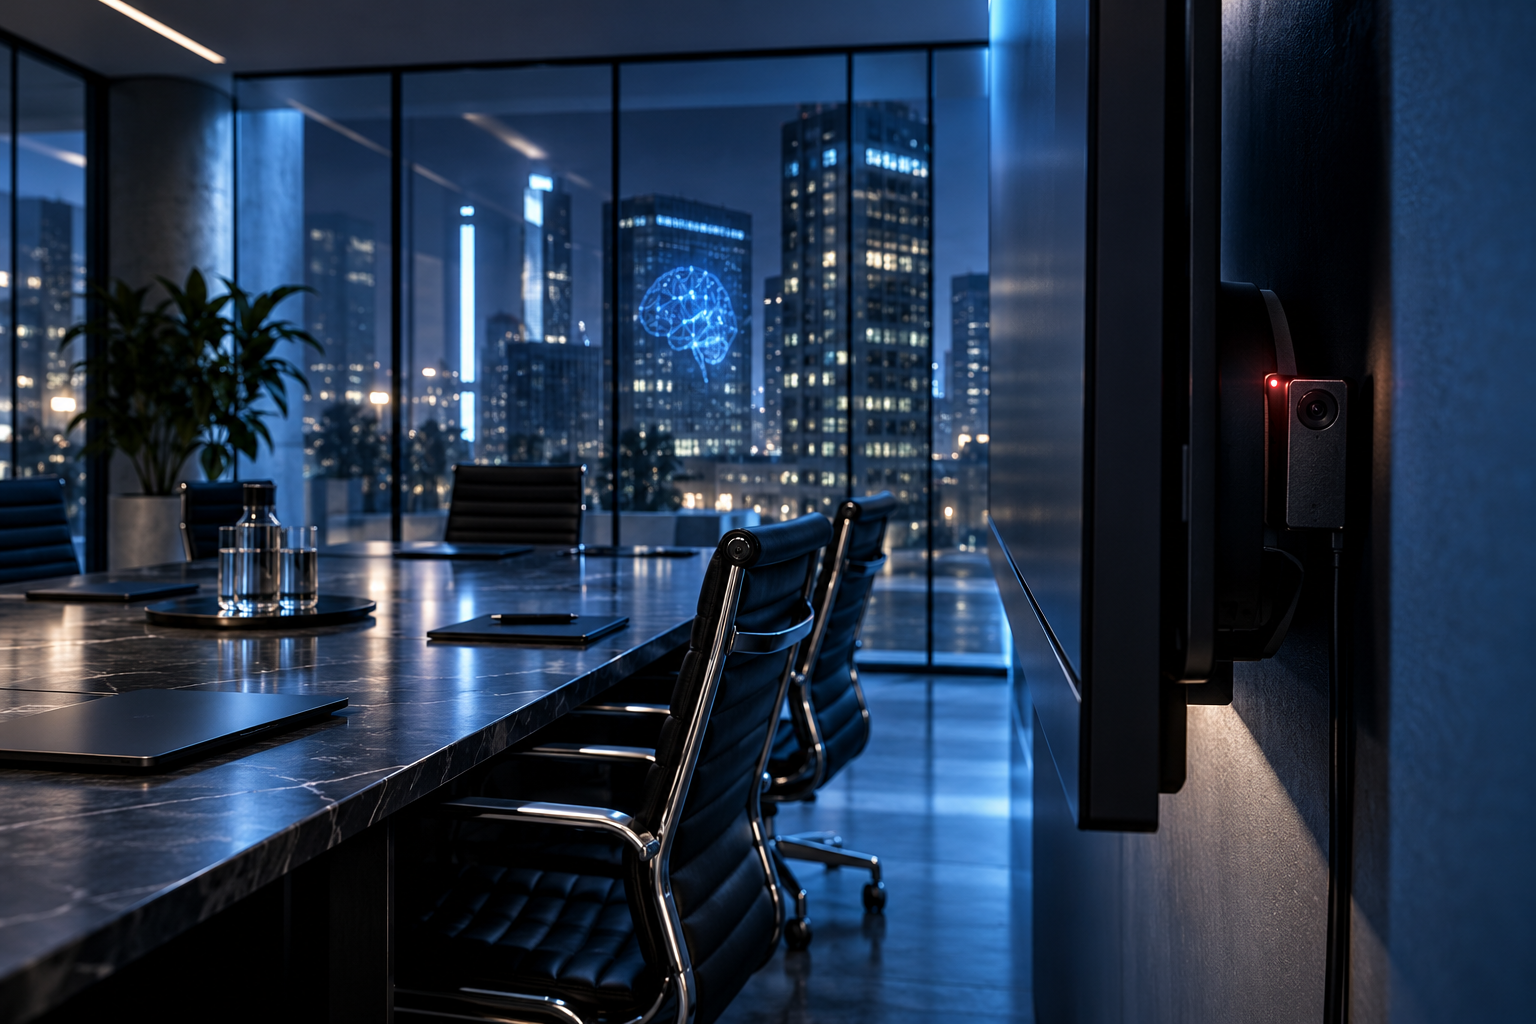
Last week, an OpenAI engineer named Abdulrahman Alfozan walked into an executive conference room at the company’s San Francisco headquarters, plugged a thumb-sized recording device into a USB port on the back of a television, and concealed it behind toilet paper. He didn’t have access to that room. He wasn’t supposed to be there. But he had a plan: capture sensitive conversations about OpenAI’s super intelligence technology and, if the FBI is right, use them for purposes the company still hasn’t fully explained.
Alfozan was arrested on October 9. The FBI charged him with using an electronic device to intercept oral communications. He faces up to five years in prison and a $250,000 fine. The case is still unfolding, but the details already public read like a spy novel set in the middle of the AI arms race.
What Actually Happened
According to the criminal complaint filed in federal court, OpenAI discovered the recording device on September 30 during a routine sweep of its executive conference room. The device had been installed two days earlier, on or about September 28. It was encrypted, audio-capable, and designed to evade monitoring.
OpenAI’s security team pulled CCTV footage and spotted Alfozan near the conference room on multiple dates before the device was found. He had no authority to access that space. When security personnel searched his bag, they found a second recording device similar to the one planted behind the TV.
Here’s where it gets interesting: OpenAI says it used its own AI models to analyze the device, understand where it came from, and identify the employee who planted it. The company referred the matter to the FBI, which moved quickly to make an arrest. FBI Director Kash Patel said the scheme was to “capture sensitive communications about the company’s super intelligence technology.”
OpenAI has stated it found no evidence that Alfozan accessed or exfiltrated model weights, source code, or customer data. He was terminated. But the fact that a single engineer could walk into a restricted executive area, plant a hidden recording device, and nearly get away with it raises uncomfortable questions about insider risk in the AI industry.
The Insider Threat AI Companies Weren’t Ready For
This isn’t just an OpenAI problem. It’s an industry problem wearing an OpenAI badge.
AI companies are sitting on the most valuable intellectual property of the 2020s. Model architectures, training techniques, safety research, product roadmaps, government engagement strategies — the stuff that determines who wins the next decade of computing. And the people with access to that information are often young engineers, some of whom joined the industry recently and may not fully grasp the weight of what they’re privy to.
Alfozan had been at OpenAI since July 2025. That’s barely over a year. He was a product team engineer, not a senior researcher or executive. Yet he had physical access to areas where the company’s most sensitive strategic discussions took place. That’s a failure of access controls, not just individual judgment.
The AI industry has spent enormous energy worrying about external threats — nation-state hackers, cybercriminals, model theft via API abuse. But the insider threat is arguably harder to defend against because insiders already have legitimate access. They know where the cameras are. They know which rooms matter. They know when security sweeps happen.
This case also lands against the backdrop of OpenAI’s own trust problems. Earlier this year, the company fired safety researchers who then warned about a chilling effect on AI safety culture. The irony of an insider allegedly spying on the same company that just gutted its safety oversight is hard to miss. If you’re an employee watching your colleagues get fired for raising concerns, what does that do to your own calculus about what’s acceptable?
What This Means for AI Security
There are three lessons here that every AI company should take seriously.
First, physical security is still security. We live in an era of zero-trust architecture, endpoint detection, and AI-powered threat analysis. But a $50 recording device hidden behind toilet paper defeated all of that. The weakest link in any security chain is always the physical layer. If someone can walk into a room and plug something into a USB port, your digital defenses don’t matter.
Second, access controls need to be tighter. Alfozan had no business being in that executive conference room. The fact that he could appear there on multiple occasions without being challenged suggests a culture of loose physical access. In government facilities, this would be unthinkable. In AI companies where the stakes are just as high, it should be too.
Third, the AI industry needs to take insider risk as seriously as it takes external risk. Companies like OpenAI, Anthropic, and Google DeepMind are handling technology that governments consider matters of national security. Microsoft is already thinking about this — Satya Nadella has called for AI models to have an emergency brake. The FBI’s swift response — and Patel’s explicit framing of the case as a counterintelligence priority — makes that clear. If the U.S. government treats AI secrets as national security assets, AI companies need to structure their security programs accordingly.
The Trust Deficit
This case lands in the middle of a broader trust crisis in AI. The same company that fired safety researchers earlier this year is now dealing with an insider who allegedly tried to spy on its most sensitive discussions. Anthropic has taken similarly drastic measures — cutting off internet access for its AI agents during evaluations. The pattern is hard to ignore: a company that doesn’t trust its own employees enough to hear safety warnings now discovers it couldn’t trust one of them to respect a conference room.
AI companies are asking the public to trust them with increasingly powerful systems. The AI trust war is already underway — and data centers are dropping NDAs to rebuild confidence. They’re asking governments to regulate them lightly. They’re asking employees to work on technology that could reshape the global order. But trust is earned, not claimed. And a company that can’t keep its own conference rooms secure has a trust problem that no amount of safety research or public relations can fix.
The broader industry should pay attention. If this can happen at OpenAI — the best-funded, most scrutinized AI company in the world — it can happen anywhere. And the next time, the person behind the device might not get caught on CCTV.
The Geopolitical Dimension
There’s another layer here that hasn’t gotten enough attention. Alfozan is a Saudi national. Saudi Arabia has been aggressively investing in AI as part of its Vision 2030 economic diversification plan, and the kingdom’s sovereign wealth fund has been one of the most active investors in AI companies globally. The Saudi government’s AI ambitions are well-documented, and the country has been building domestic AI capabilities at a rapid pace.
Now, let me be clear: there is zero evidence that the Saudi government was involved in this case. The DOJ has not suggested any foreign state sponsorship. Alfozan acted alone, as far as we know. But The optics are terrible for OpenAI. The company is already under financial pressure — a $20 billion revenue gap that raises questions about its business model. A Saudi national, hired just over a year ago, allegedly plants a recording device in the company’s most sensitive meeting room. Even if this was purely a personal scheme, the appearance of a foreign intelligence connection is inevitable.
This is the kind of case that keeps counterintelligence officials up at night. The AI industry is global, and the talent pool is international. Engineers from dozens of countries work at OpenAI, Anthropic, Google, and Meta. That’s not a bad thing — diversity of thought and experience makes better products. But it does mean that insider risk has a geopolitical dimension that domestic companies in other industries don’t have to think about as carefully.
The U.S. government has already signaled that it treats AI innovation as a national security priority. Patel’s statement about “protecting American SI innovation” makes that explicit. If AI companies want to continue hiring the best talent from around the world — and they do — they need security programs that account for the fact that some of those employees may have loyalties, financial pressures, or personal grievances that create insider risk.
My Take
As someone who manages IT systems and thinks about security daily, this case is a reminder that the human element is always the weakest link. We can build the most sophisticated digital defenses in the world, but if we don’t address physical security, access controls, and insider risk, we’re building castles with unlocked back doors.
The AI industry is moving fast. Maybe too fast. In the race to build more powerful models, companies have scaled hiring, expanded office footprints, and granted broad access to employees who joined months ago. That’s not inherently wrong — you need talent to build these systems. But talent without oversight is a liability.
I’ve said before that the AI trust war is just beginning. This case is another data point. The companies that win long-term won’t just be the ones with the best models. They’ll be the ones that can be trusted with the power those models confer. And trust starts with keeping your own house in order.
The question isn’t whether other AI companies have similar insider risks. They do. The question is whether they’ll wait for their own Alfozan moment to take it seriously.